Cyberattacks: let's stop playing one move behind
Supermarkets forced to throw away food following a cyberattack: Floriane Bonnier calls for shifting from reaction to anticipation in cybersecurity, from connected devices to the energy transition.
A refrigerator that can no longer be controlled. Food that must be thrown away. A business whose activity is disrupted by an IT intrusion. Cyberattacks are no longer an abstract threat: they reach the equipment that keeps our daily lives running.
On 2 November, incidents affecting refrigeration systems hit supermarkets across several European countries, including Belgium. Stores had to withdraw food items from sale. A few weeks earlier, refrigeration facilities had already been targeted in France. Without prejudging the conclusions of the investigations or any link between these events, their succession should give us pause.
We cannot continue discovering our dependencies at the very moment they turn into vulnerabilities.
Life is a game of chess: you do not protect your pieces merely by watching your opponent's last move. You must understand their possibilities, defend your positions, and plan several moves ahead. In cybersecurity, our ambition must be the same: shifting from reaction to anticipation.
When a digital intrusion becomes physical damage
Cybersecurity is not just about data confidentiality. It is also about the availability of equipment and the reliability of commands sent to it. When an intrusion disrupts a store's refrigeration, the consequences do not remain on a screen: they impact goods and economic activity.
Our security policy must therefore answer three questions. How do we prevent an intrusion? How do we maintain essential missions when one occurs nonetheless? And how do we swiftly restore secure operations?
Promising that no attack will ever succeed would be irresponsible. Our goal must be to reduce intrusion opportunities, limit damage, and organise recovery before the crisis, not during it.
Connected devices must stop being a blind spot
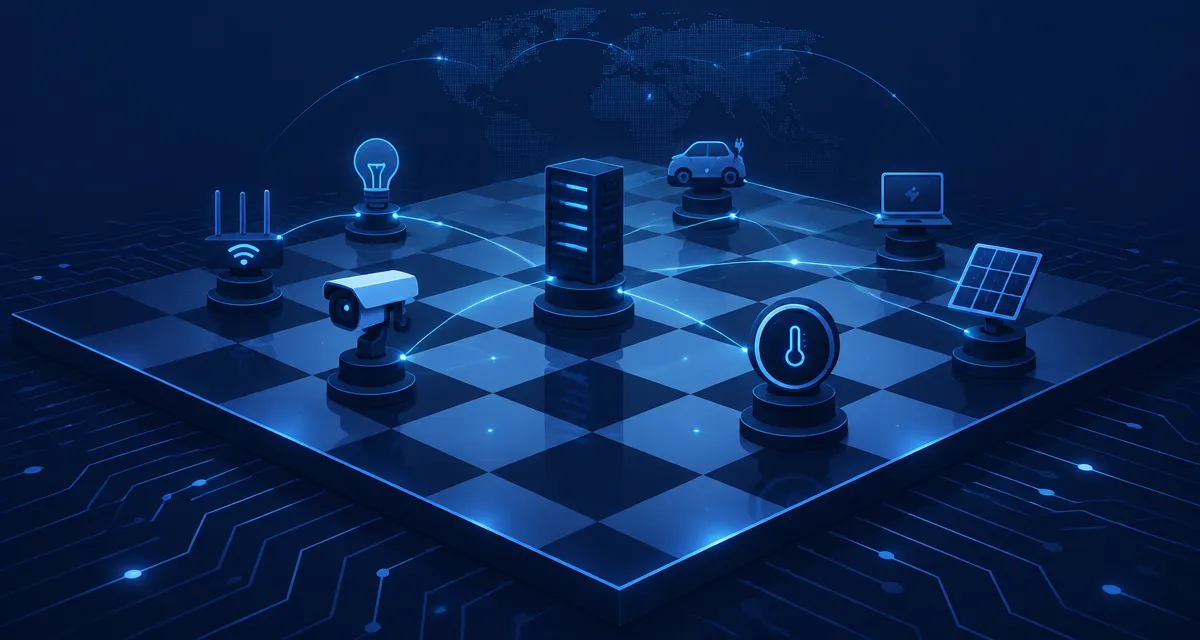
Cameras, heating systems, refrigeration units, access control: protecting technical equipment calls for a specific approach, tailored to their functions and the physical consequences of a failure. Recommendations from ANSSI and CISA particularly emphasise device inventory, network segmentation, and control over remote access.
We must translate these principles into clear and verifiable requirements.
First requirement: knowing what is connected. Every organisation must be able to identify its critical equipment, its software, support duration, and the service providers who can access it. How can an organisation properly protect a device when it is unaware of its existence or access routes? An inventory is a first line of defence, not an administrative formality.
Second requirement: segmenting networks. A refrigeration system must not have unrestricted access to administrative computers; a camera must not be able to serve as a gateway to an energy facility. Uses must be separated and communications between them monitored. The principle is simple: block by default, then allow only necessary exchanges. Creating a separate network is not enough if all doors remain open between networks.
Third requirement: retaining control over interventions. Remote maintenance is useful, but it must not become permanent and uncontrolled access. Accounts must be individualised, privileges limited, connections secured with strong authentication, and interventions traceable. When a service provider no longer requires access, it must be possible to revoke it.
Finally, security must be maintained over time. Patches, anomaly monitoring, and the replacement of equipment that can no longer be kept secure must be organised. For sensitive installations, these operations must be planned with the operator: a poorly managed change can itself disrupt operations.
These measures do not promise invulnerability. They aim to prevent a compromised device from becoming the starting point for a much wider disruption.
Energy: securing the transition, not slowing it down
This requirement takes on a special dimension in energy. Experts from the Smart Energy Expert Group, who advise the European Commission, have identified risk scenarios involving, in particular, manufacturers' digital platforms, remote access, and photovoltaic installation networks. Their warning concerns the potential to disrupt multiple pieces of equipment simultaneously. These are identified risks, not proof that an attack of such scale has occurred.
It would be absurd to conclude that we must abandon solar energy. It would be equally reckless to deploy equipment without questioning who can control it, update it, or modify its settings.
The question is not choosing between energy transition and security. It is making security a condition for the transition's success.
We must ask, right from procurement, who controls remote access, how updates are secured, and what functions remain available if an external platform becomes unreachable. For critical equipment, the ability to maintain local control and operate under degraded conditions must be assessed and tested with operators.
Energy sovereignty must also be measured by our ability to retain control over the equipment that generates and manages our electricity.
Neither naivety nor prejudgement
The European Union has begun to act. In the spring of 2026, the Commission initiated funding restrictions for projects using inverters from suppliers deemed high-risk. In October, experts from the Smart Energy Expert Group recommended going further. However, these recommendations do not constitute a blanket ban already in effect.
The debate deserves better than a crude division between Chinese and European equipment. Nationality alone cannot serve as a security assessment. Yet neither should we disregard the jurisdiction to which a supplier is subject, its ownership structure, or effective control over command functions.
Our line must be clear: transparent criteria, verifiable safeguards, and proportionate restrictions when risks warrant them. European experts themselves stress that any restriction must be based on thorough analysis and take available alternatives into account.
Security must be neither a protectionist pretext nor the adjustment variable of the lowest bidder.
From obligations to evidence
Claiming that nothing was anticipated would be inaccurate. In Belgium, most provisions of the NIS2 framework have applied since 18 October 2024. For the entities concerned, this framework notably covers risk management, notification of significant incidents, and obligations for management bodies. Business continuity, backups, and recovery are among the requirements.
However, our political standard cannot stop at the mere existence of a law or a plan. It must focus on their operational implementation.
A backup must be able to be restored. A continuity plan must be executable. A network presented as segmented must genuinely be so. A chain of responsibility must be understood by those who will have to act at three in the morning.
I therefore advocate three priorities for public action.
First, embedding security into procurement. For sensitive equipment, contracts must stipulate support duration, maintenance terms, access management, vulnerability notification, and exit options. We must compare total costs, not just the advertised price.
Second, pooling expertise. Municipalities and small organisations must be able to access shared expertise to inventory their equipment, secure their networks, prepare procurement contracts, and run crisis simulations. Demanding more without providing access to the necessary resources would not be a credible policy.
Finally, measuring results. How many critical assets are inventoried? Which remote access points have been audited? Have backups been restored during a test? How long does it truly take to restore a service? Have identified weaknesses been remediated? These are the questions we must ask, without publicly disclosing details that could assist an attacker.
Regaining the initiative
We must neither sensationalise without evidence nor normalise out of habit. We must decide that the continuity of essential services is a leadership responsibility, that security is part of an asset's quality, and that a digital investment is not judged solely by what it allows when everything is functioning.
It is also judged by what it manages to safeguard when something goes wrong.
In chess, the player who only responds to threats allows the other to dictate the game. We have no more time to waste commenting on the last move. We must plan the next ones — and regain the initiative.
Gallery